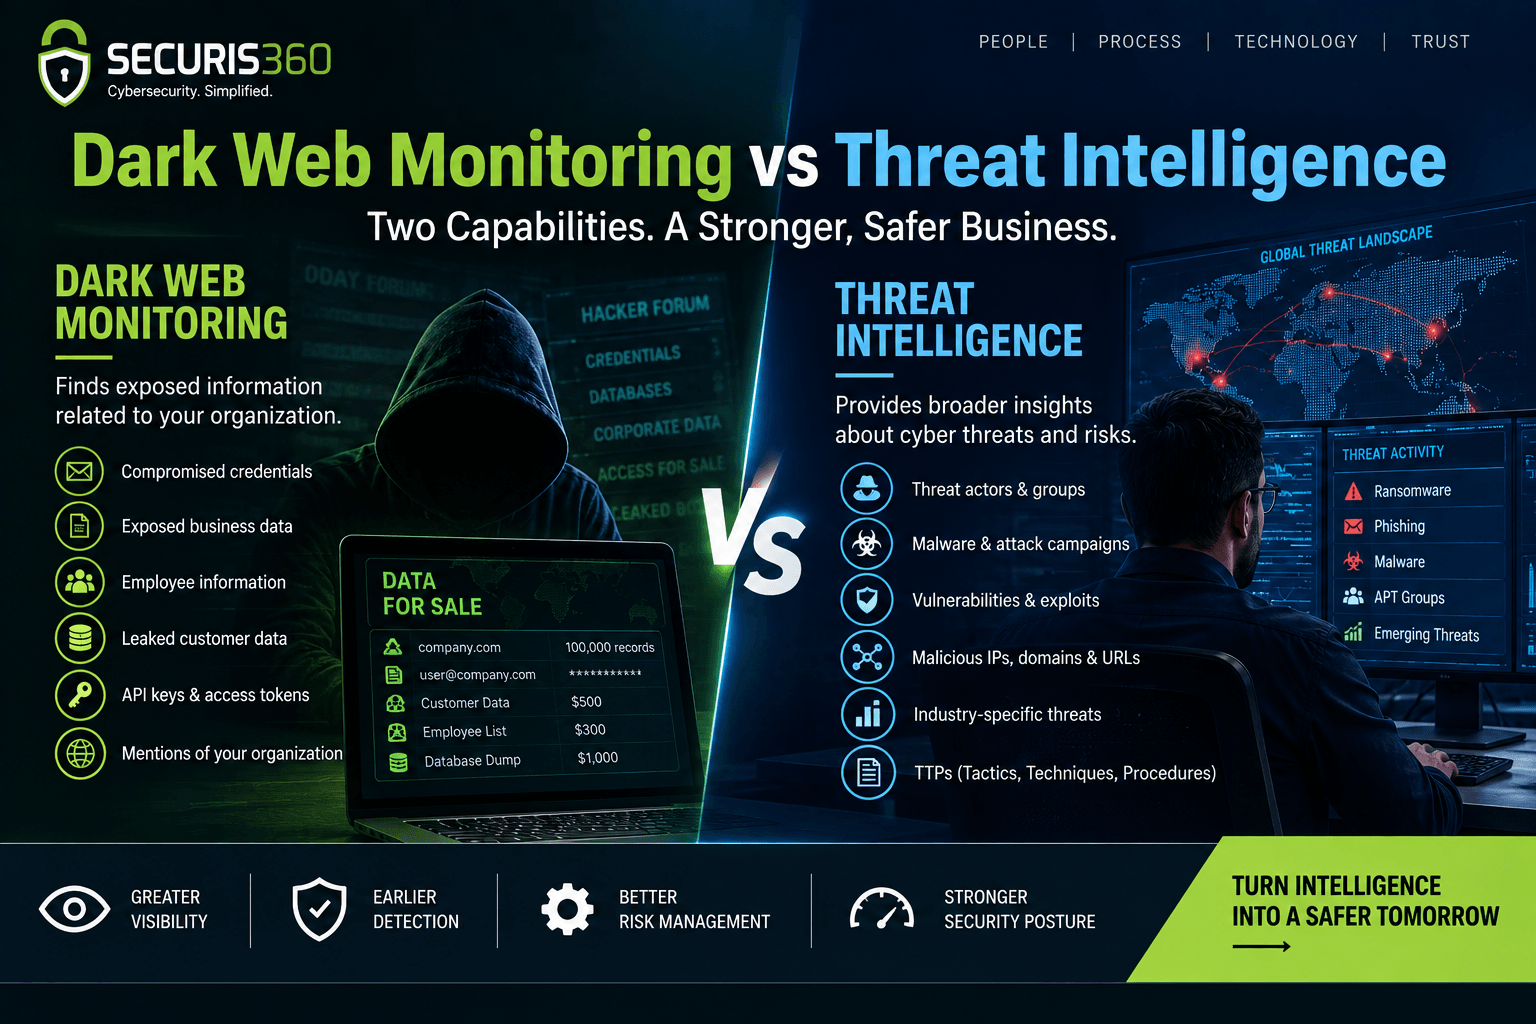
Dark Web Monitoring vs Threat Intelligence: What’s the Difference?

Cybersecurity teams need visibility beyond what is happening inside their own networks. An organization may have firewalls, endpoint protection, SIEM, vulnerability management, and other security controls in place, but attackers can still expose business information outside the organization’s direct environment. This is where Dark Web Monitoring and Threat Intelligence become valuable. These two capabilities are […]
READ MORE
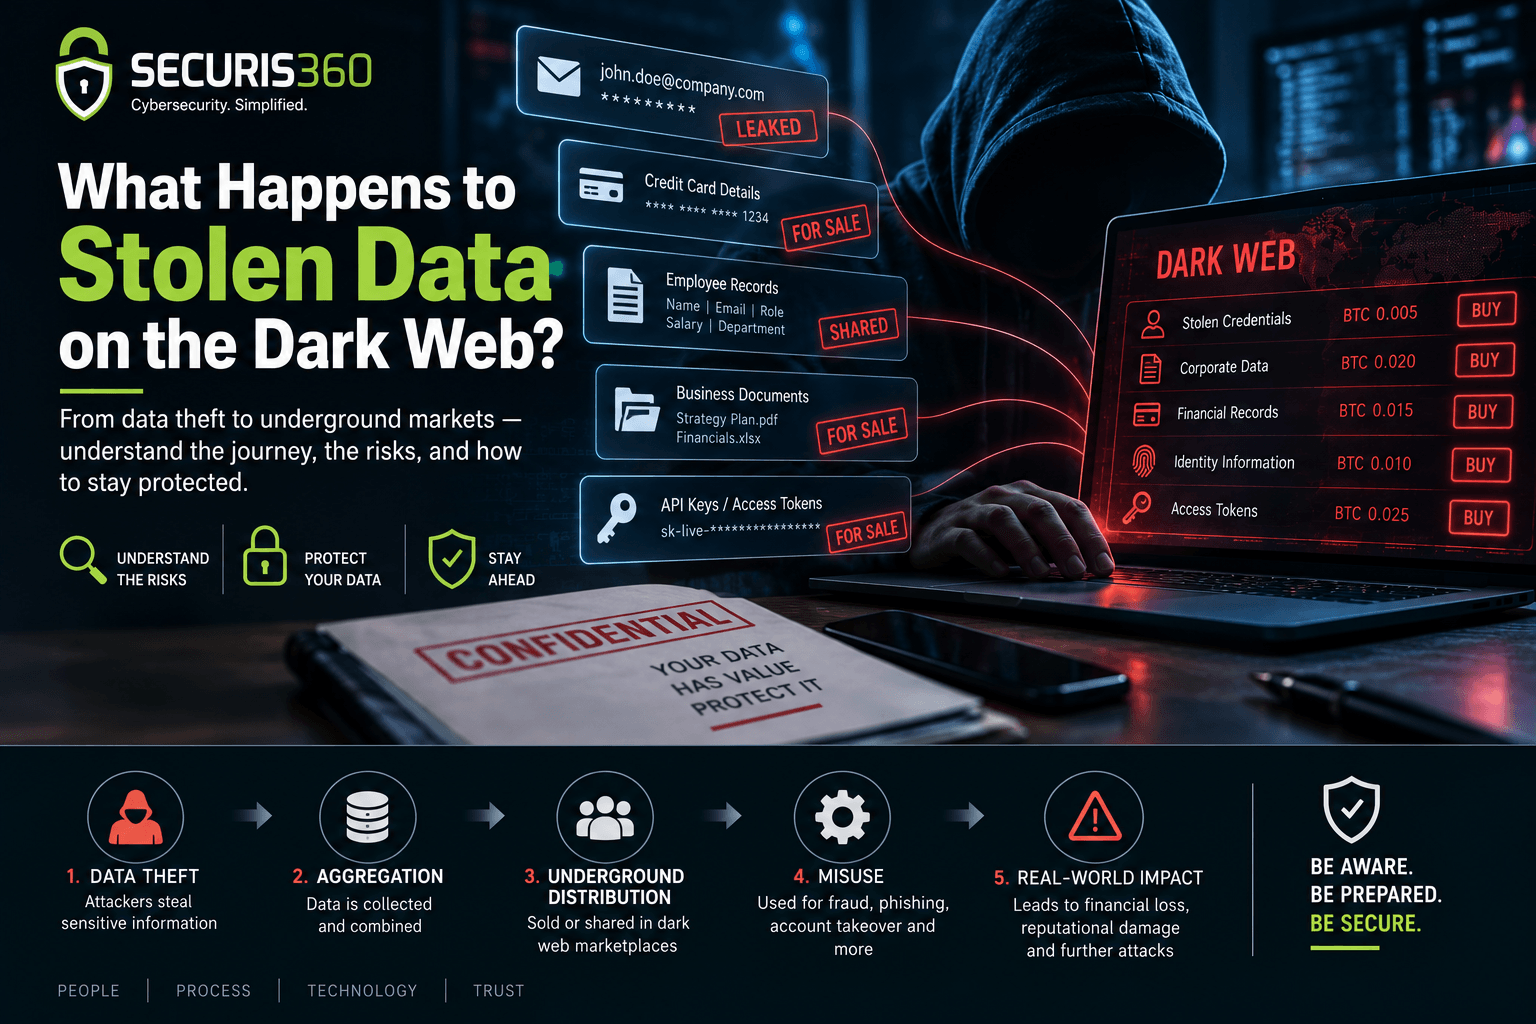
What Happens to Stolen Data on the Dark Web?

When a cyberattack exposes sensitive information, the damage does not necessarily end when the attacker leaves the compromised system. Stolen information can move into underground online communities, where cybercriminals may sell, exchange, reuse, or combine it with other information to support additional attacks. Passwords, email addresses, customer records, financial information, corporate documents, session information, and […]

READ MORE
Dark Web Monitoring for Small Businesses: What You Need to Know

Small businesses are increasingly targeted by cybercriminals because they often hold valuable customer, employee, financial, and business information but may have fewer cybersecurity resources than large enterprises. A compromised password, leaked email address, exposed API key, or stolen business document can give attackers an opportunity to target an organization. One way businesses can improve their […]

READ MORE
How AI Improves Security Operations Centers

Security Operations Centers (SOCs) are responsible for monitoring an organization’s technology environment, detecting suspicious activity, investigating threats, and responding to security incidents. But modern organizations generate enormous amounts of security data every day. Cloud platforms, endpoints, applications, identity systems, firewalls, SaaS applications, and network infrastructure continuously produce logs and security events. For security teams, reviewing […]

READ MORE
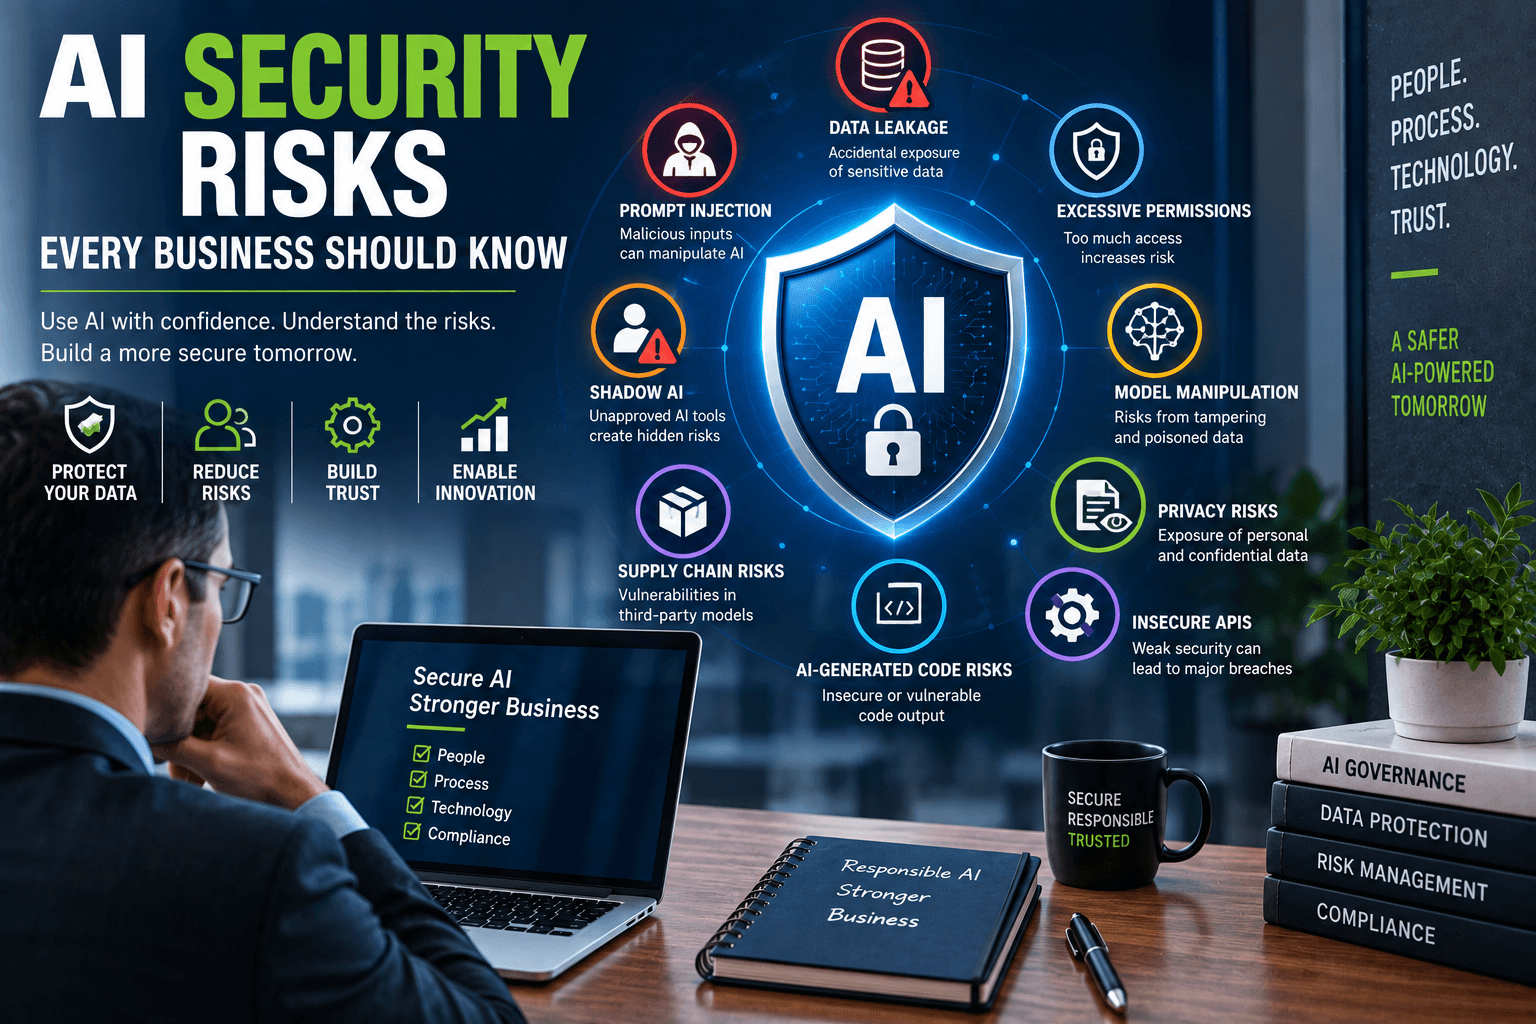
AI Security Risks Every Business Should Know

Artificial intelligence is changing how businesses work. Organizations are using AI for customer support, software development, marketing, fraud detection, data analysis, document processing, healthcare applications, financial services, and internal operations. But while AI can improve productivity, it also introduces new cybersecurity risks. An employee can accidentally enter confidential information into an AI tool. A malicious […]

READ MORE
How SOC 2 Helps You Close Enterprise Deals Faster

The Real Reason Enterprise Deals Stall Ask any B2B sales leader where their biggest deals get stuck, and the answer is rarely price or features. It’s security review. Enterprise procurement teams add 4–8 weeks to a sales cycle when a vendor can’t produce a SOC 2 report, and 30–50% of pipeline can sit stalled in […]

READ MORE
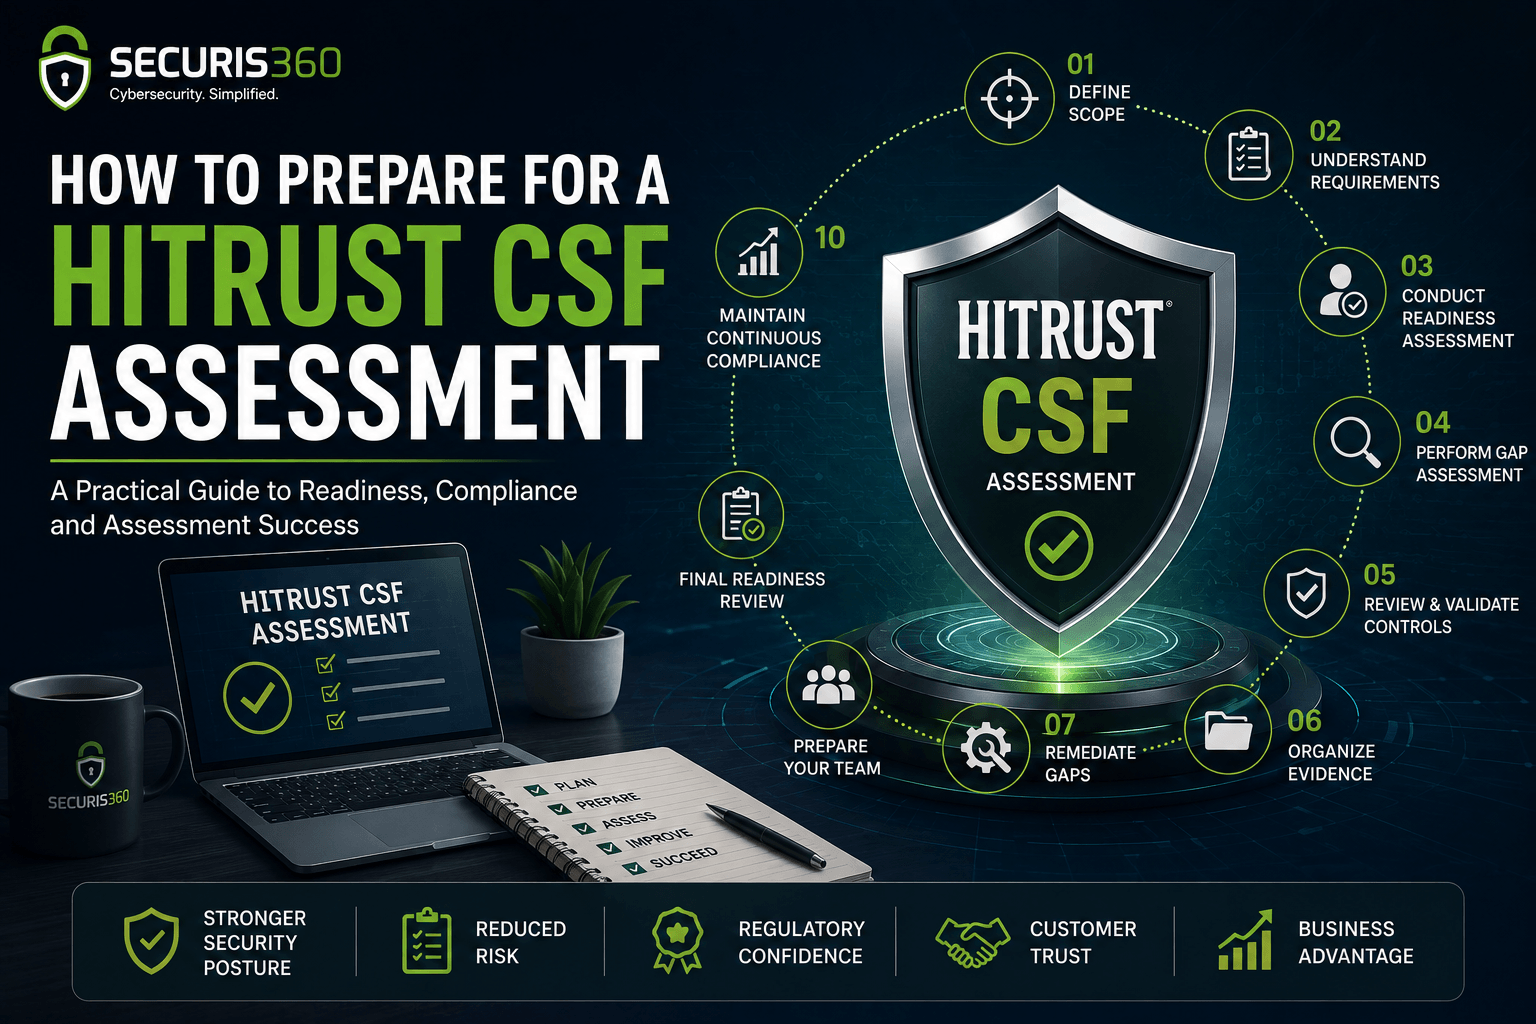
How to Prepare for a HITRUST CSF Assessment: A Practical Guide

Preparing for a HITRUST CSF assessment can feel overwhelming, especially when an organization is managing security controls, policies, technical systems, risk management, and evidence across multiple teams. The good news is that a HITRUST assessment does not have to become a last-minute compliance exercise. With proper planning, organizations can identify gaps early, improve security controls, […]

READ MORE
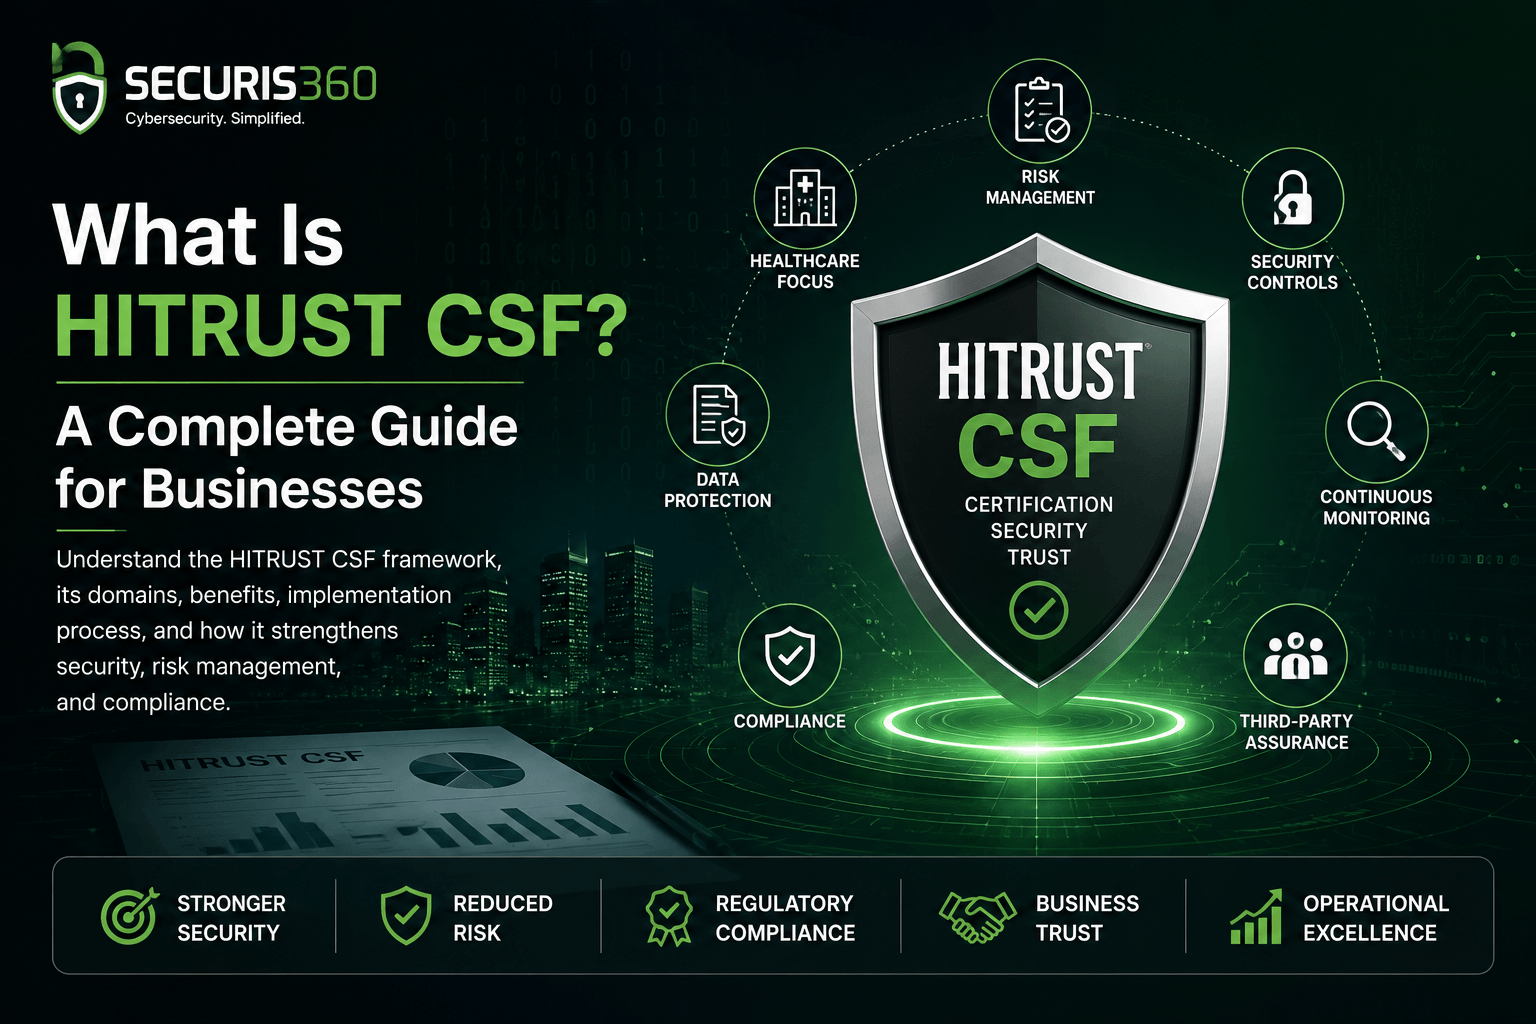
What Is HITRUST CSF? A Complete Guide for Businesses

Cybersecurity is no longer only an IT responsibility. For businesses that handle customer records, payment details, health information, or other sensitive data, security has become a major factor in winning trust, meeting contractual requirements, and avoiding costly incidents. One framework frequently requested by enterprise customers—especially in healthcare, technology, financial services, and third-party vendor environments—is the […]

READ MORE
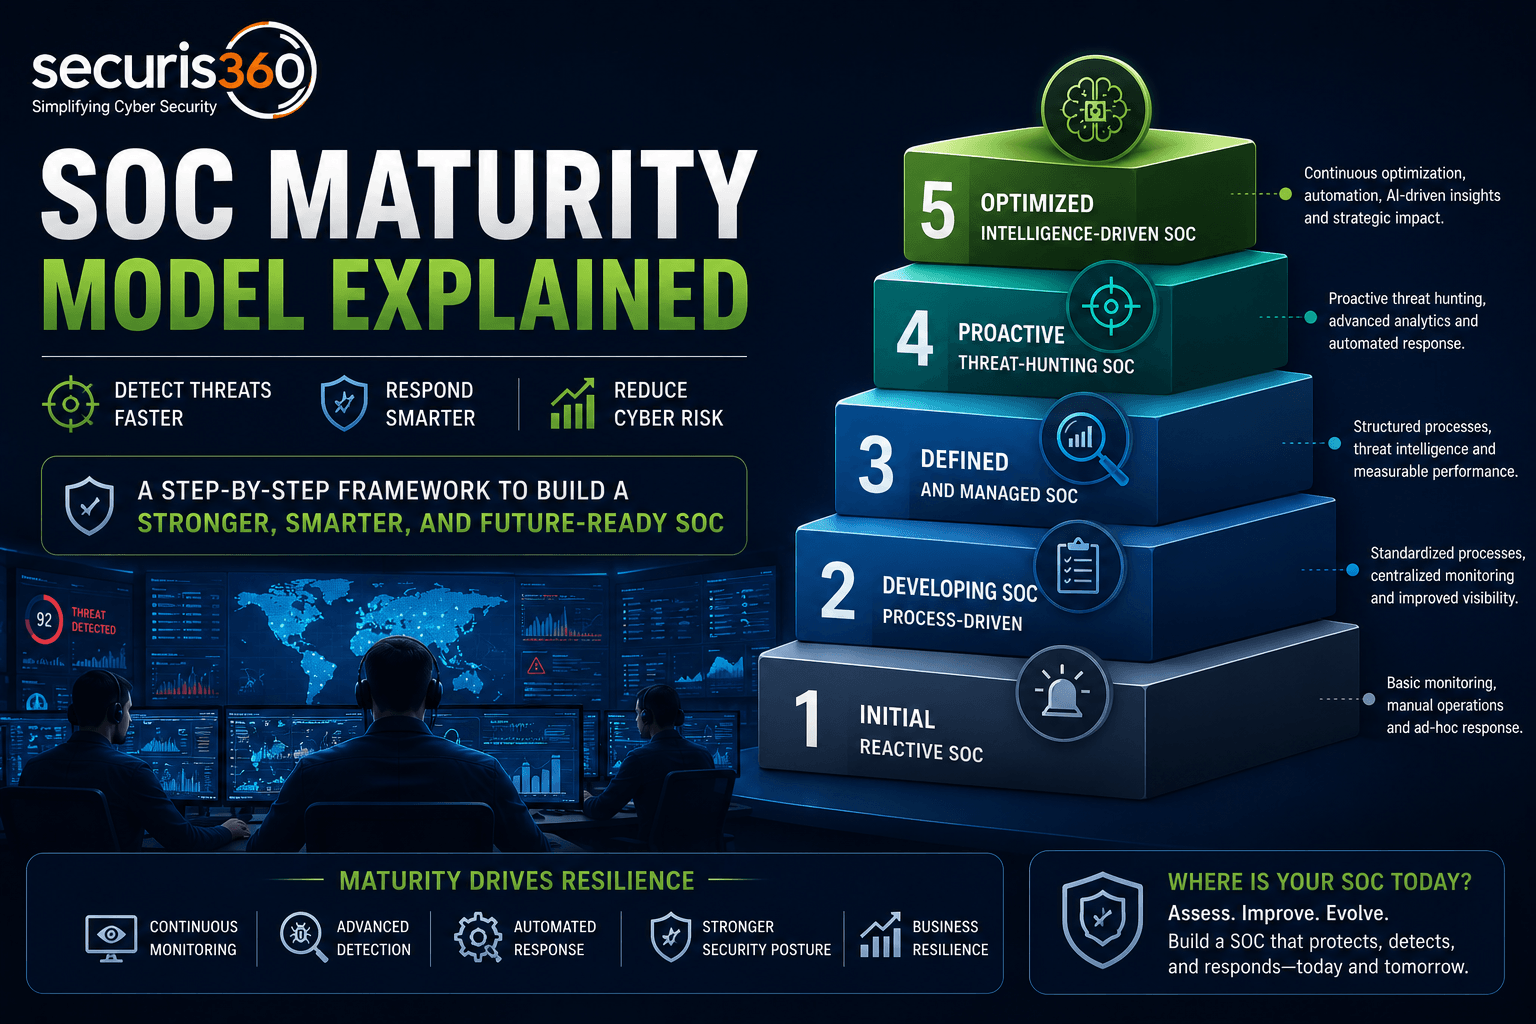
SOC Maturity Model Explained: A Complete Guide for Modern Businesses

A Security Operations Center (SOC) is responsible for monitoring, detecting, investigating, and responding to cybersecurity threats. But simply having a SOC does not automatically mean an organization has a mature security operation. A mature SOC continuously improves its ability to detect threats, investigate incidents, automate response, hunt for attackers, and provide meaningful security intelligence to […]

READ MORE
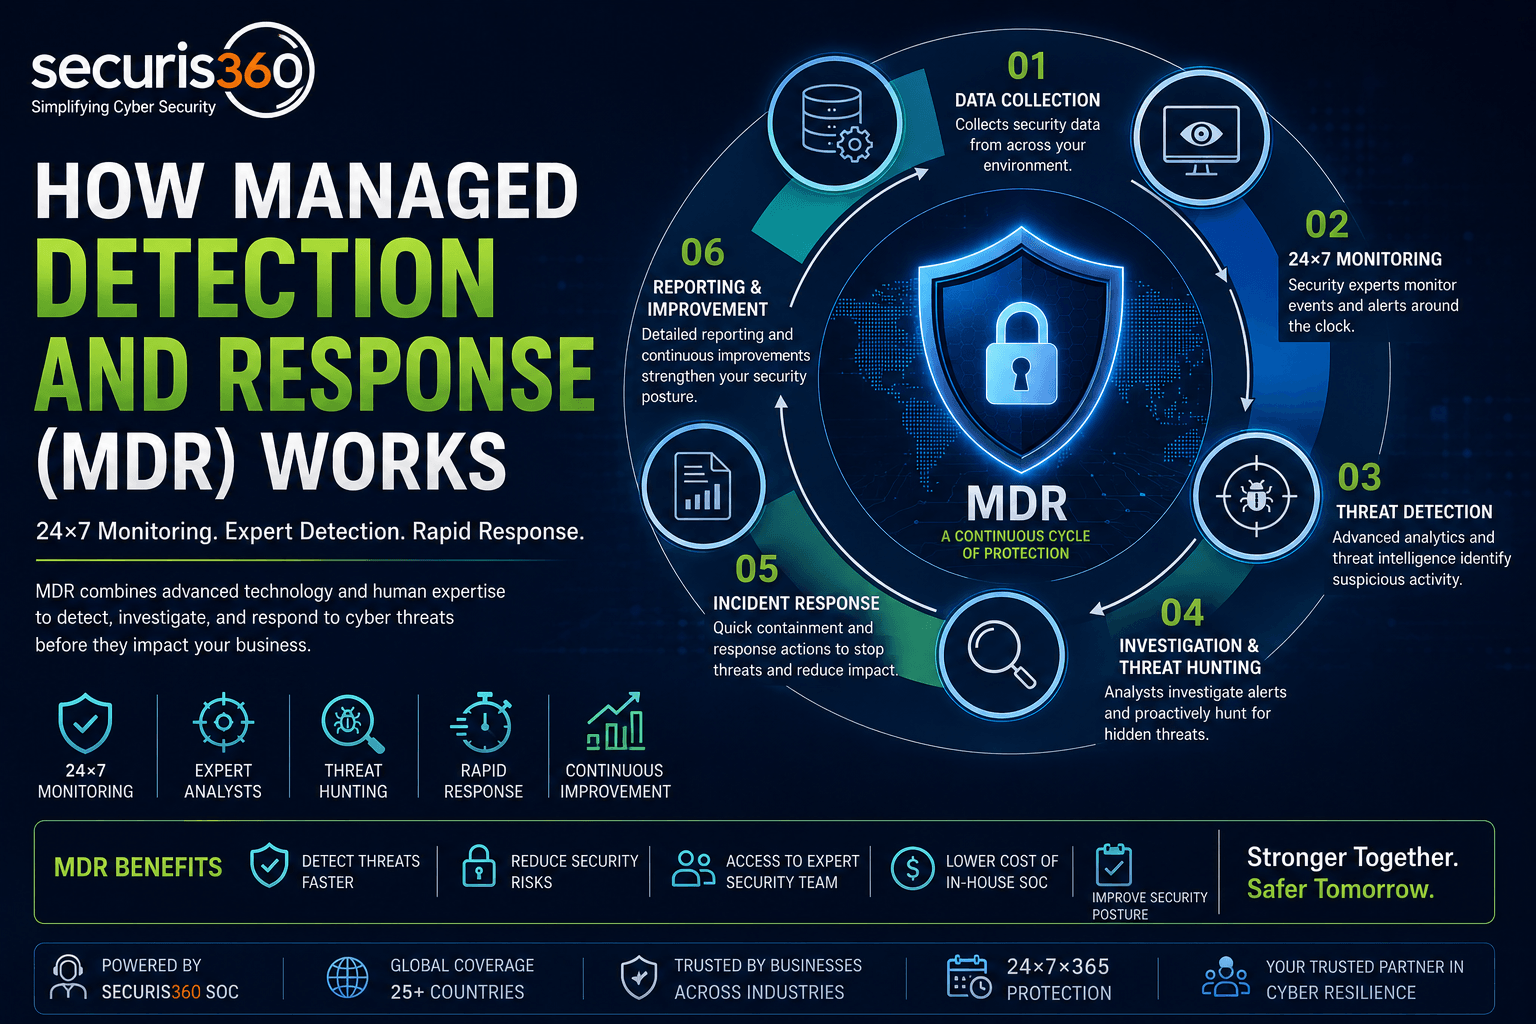
How Managed Detection and Response (MDR) Works: Complete Guide

Cyber threats are becoming more sophisticated, while security teams are expected to monitor increasingly complex environments across endpoints, cloud infrastructure, applications, identities, and networks. Simply deploying security tools is not enough. Organizations need people, processes, and technology working together to identify threats, investigate suspicious activity, and respond quickly. This is where Managed Detection and Response […]

READ MORE